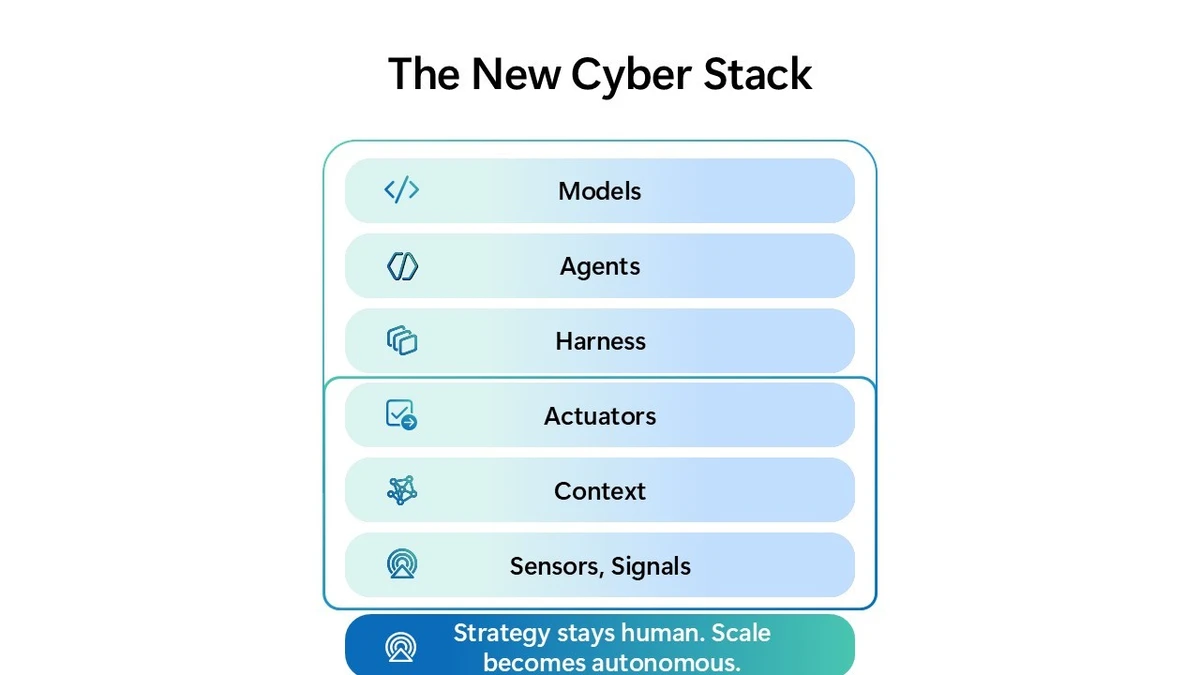
Microsoft announced an integrated security operations center (ISOC) in Microsoft Defender, describing it as a shared foundation for security information and event management (SIEM), threat protection, and agent-assisted investigations. The company says the design brings signals, context and controls together so people and agents can investigate and act from the same environment.
A unified operating layer
Microsoft presents ISOC as an alternative to stitching together separate protection and operations systems. Its description groups sensors and signals, context, models, a harness, agents and actuators into a loop that can support continuous detection and response while people set priorities and retain judgment.
Preview status matters
Microsoft says ISOC in Defender is available in preview. The announcement explains the intended architecture and workflows but provides no independently audited measurements of detection lift, response time or customer outcomes. Those results remain to be established outside the vendor’s description.